Entersekt Mobile Authentication

Beyond Protection. Engineering Trust

1 in 3

Banking apps rely on invalid auth implementations

80%

Of SIM-swap fraud attempts are successful

69%

Of clients use mobiles for banking

The era of vulnerable logins and fragmented defenses ends here 

In today's digital landscape, the mobile app is the heart of the customer experience for financial institutions (FIs). Yet, legacy authentication methods – from vulnerable usernames and passwords to the widely exploited SMS OTP (prime targets for SIM-swap fraud) – are failing to keep pace with sophisticated attackers.

Adding to the challenge, stringent regulations like PSD2 and GDPR demand robust, futureproof security.

Many solutions merely add layers of friction, forcing customers through cumbersome processes that lead to frustration and abandonment. 

At Entersekt, we don't just add layers of protection; we fundamentally redefine it. 

With Entersekt’s Mobile App Authentication, you're not just securing your app; you're joining the leaders who are actively dismantling the ecosystem in which fraud thrives. Your customers get a secure, intuitive, bank-grade experience, and you get the peace of mind that comes from being steps ahead of the threat. 
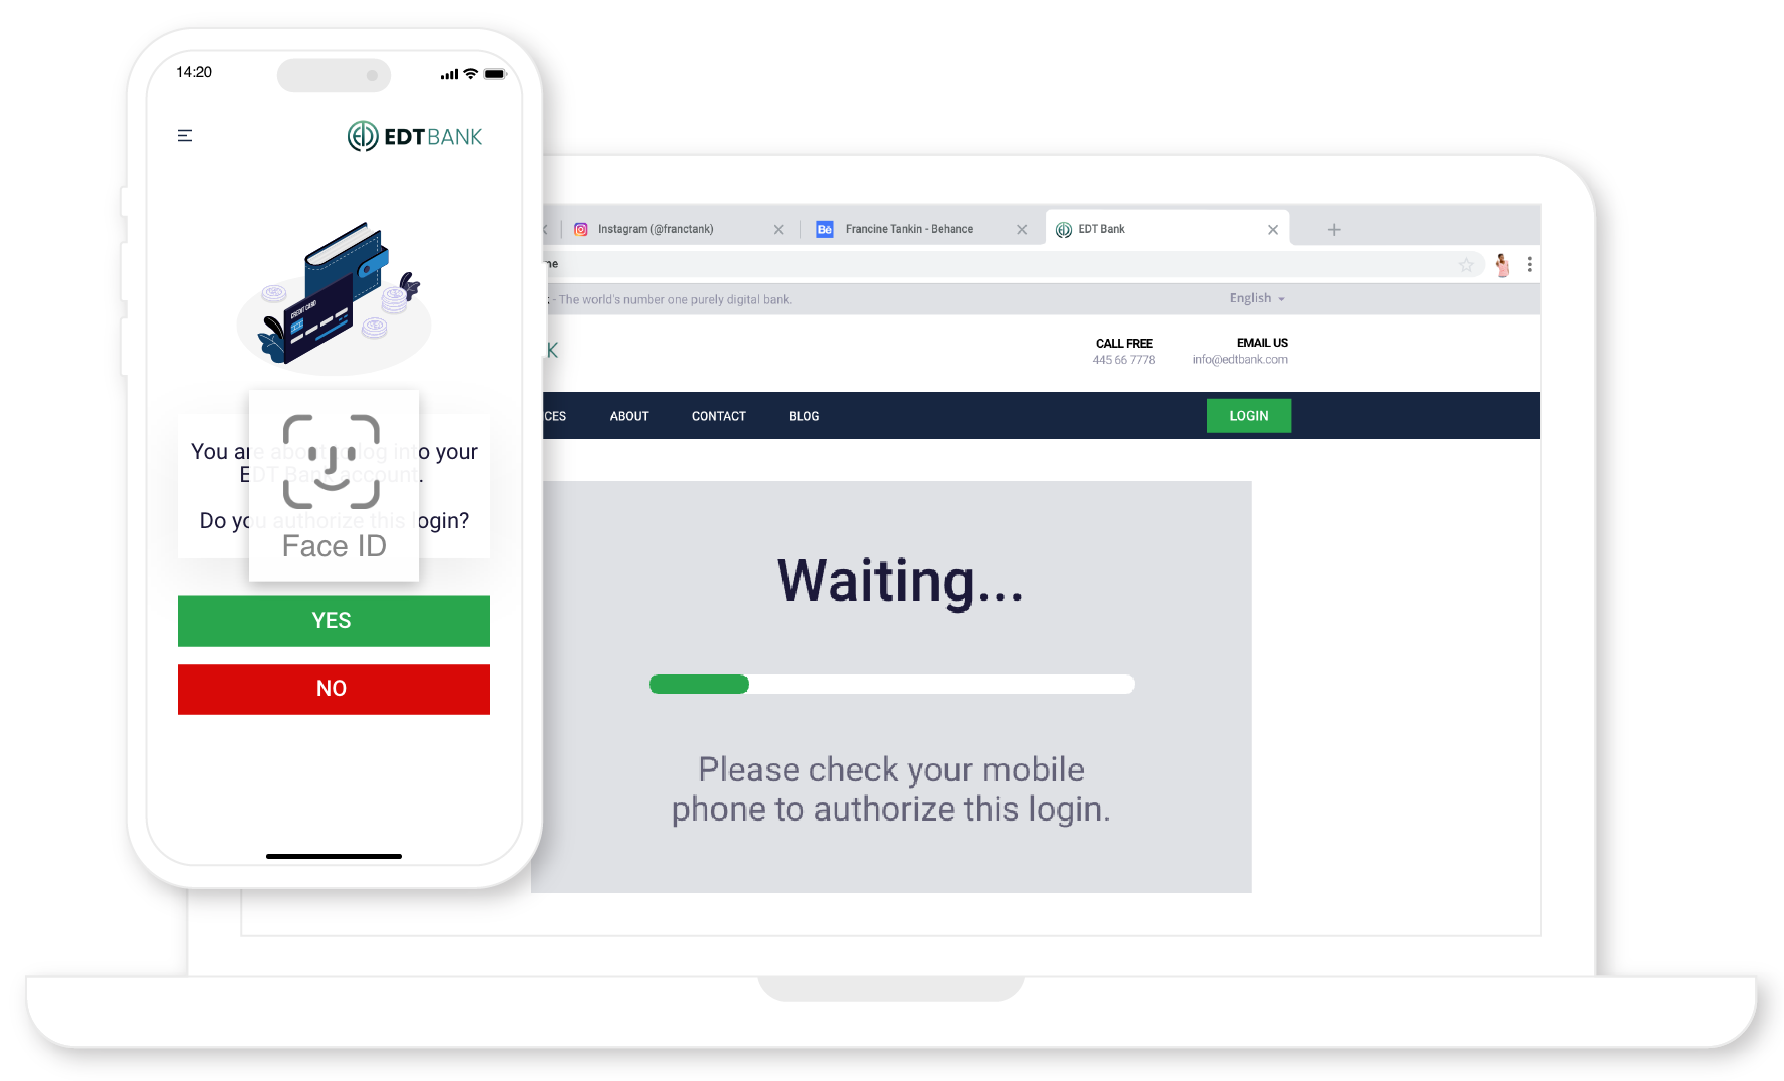
mobile-authentication-brochure

Real customer successes:

  • Virtually exterminated account takeover (ATO) fraud, because we eliminate the weakest links that fraudsters exploit.
  • Optimal customer journeys with minimal friction that elevate client trust and satisfaction. 98% of logins on average are frictionless.
  • Superior support and resources, and fast deployment, built for banking.

One unified platform. Unyielding security

Entersekt offers a single, cross-channel platform for secure authentication that redefines what’s possible in digital banking. Our approach is holistic, intelligent, and designed for tomorrow's threats.

Our solutions don’t just ask ‘Is this the customer?’ They also consider whether the customer should be performing a transaction in the first place, making fraudsters’ new social engineering tactics ineffective.

We provide consistent authentication options across all your channels, leveraging both silent and active authentication methods, as well as passwordless options including biometrics and passkeys.

The power of precision: Features that outsmart fraudsters


mobilesdk Uniquely identify and trust the customer's mobile device: Our patented device ID goes beyond mere recognition, creating an immutable trust anchor  Asset 798 Real-time device intelligence: Get immediate information about a device's current location or integrity, enabling adaptive responses to suspicious activity 
biometric Intuitive user experience: Ensures seamless, one-touch access and transaction signing, minimizing friction while maximizing security. Your customers enjoy unparalleled ease, while we work silently in the background. safe Protection against ATO and advanced attack vectors: Thanks to robust multi-factor authentication (MFA), strong device ID, and digital transaction signing, we actively protect against threats that leverage stolen credentials, SIM swaps, and automated attacks.
Transaction signing Digital transaction signing: Customers digitally sign their responses, ensuring non-repudiation and proving intent without complexity. Risk assessment Risk-based decisioning: We provide adaptive, context-aware risk signals that feed into our Authentication Advisor, enabling intelligent, adaptive authentication decisions.


We’ve moved beyond single-use case solutions and reactive patching. Our pre-integrated, MFA options are built on our proprietary, patented technology, equipping financial institutions with the strongest possible security layer. This isn't just about protection; it's about making advanced forms of attack futile.

Our Mobile App Authentication solution leverages unparalleled intelligence to protect against the most dangerous fraud attack vectors threatening FIs today.


Ready to say goodbye to outdated, vulnerable logins and fragmented defenses? 

Book your personalized demo

Sources: 1.     An Empirical Assessment of Security Risks of Global Android banking apps      2.     Princeton University          3.     www.nimbleappgenie.com